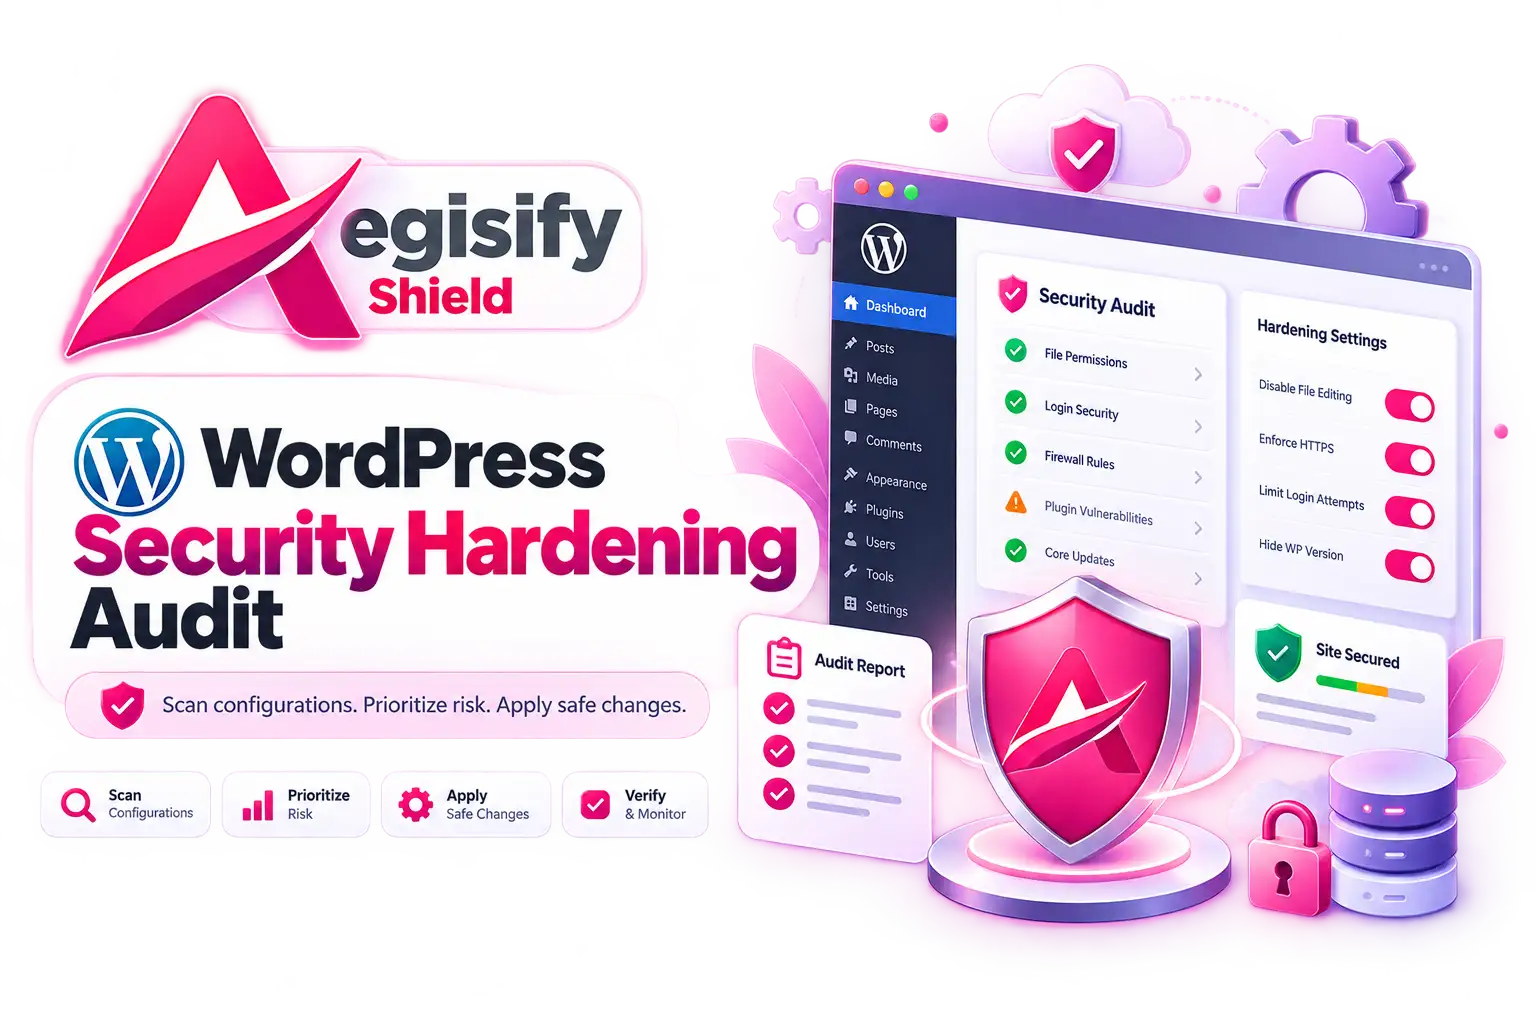
WordPress Security Hardening Audit
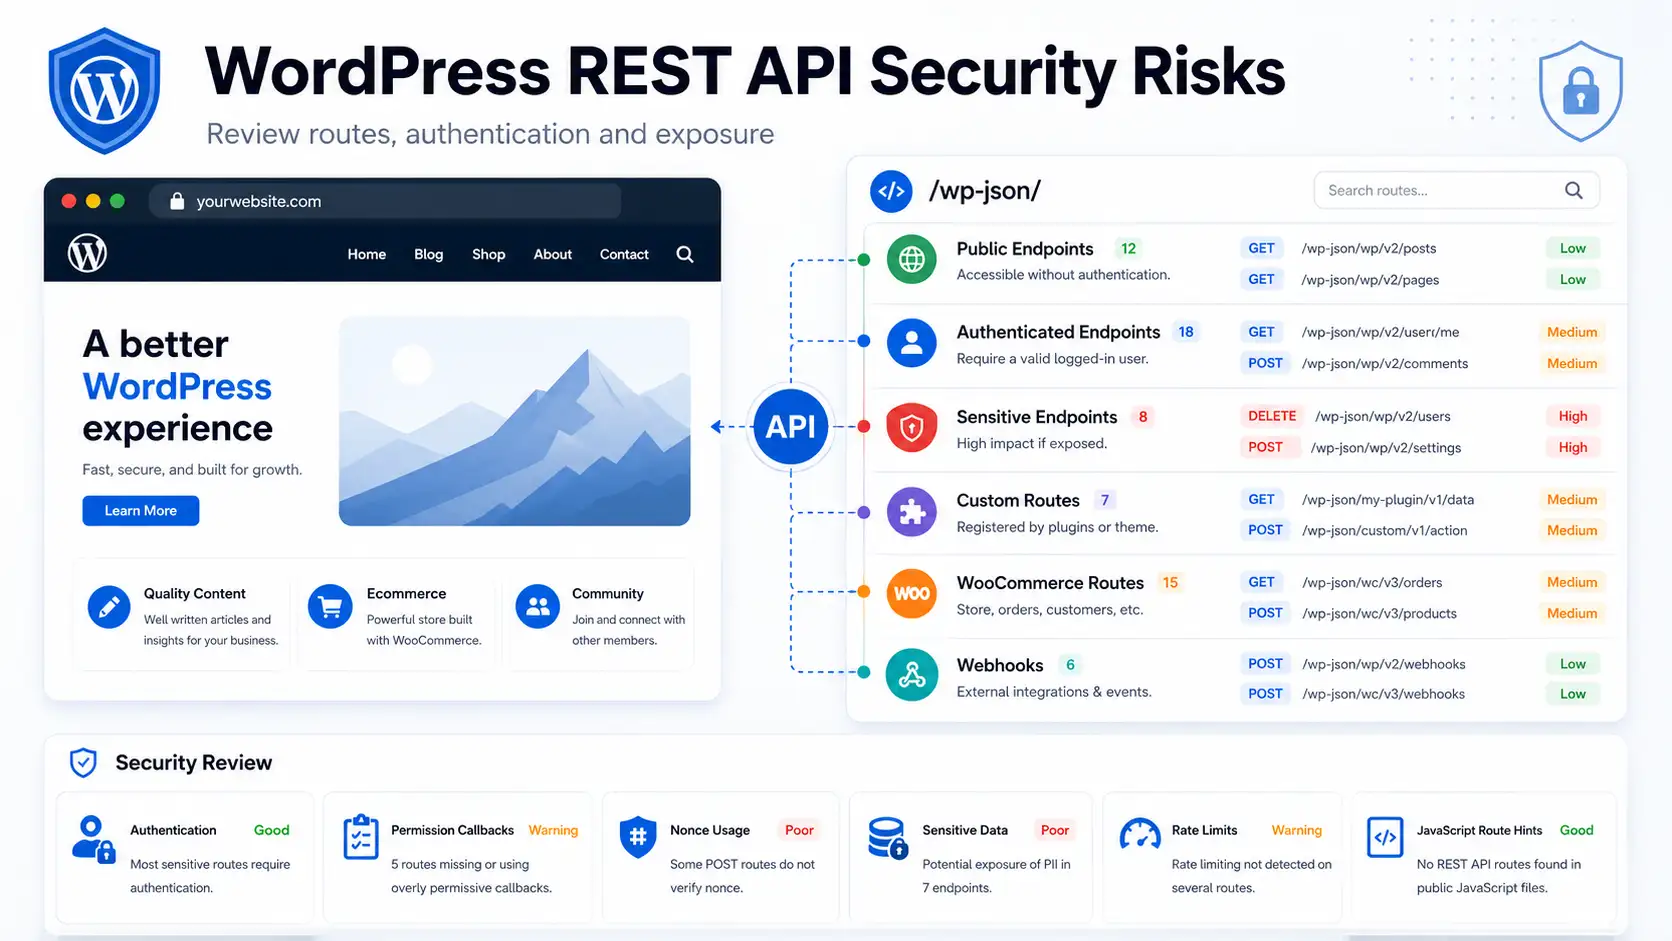
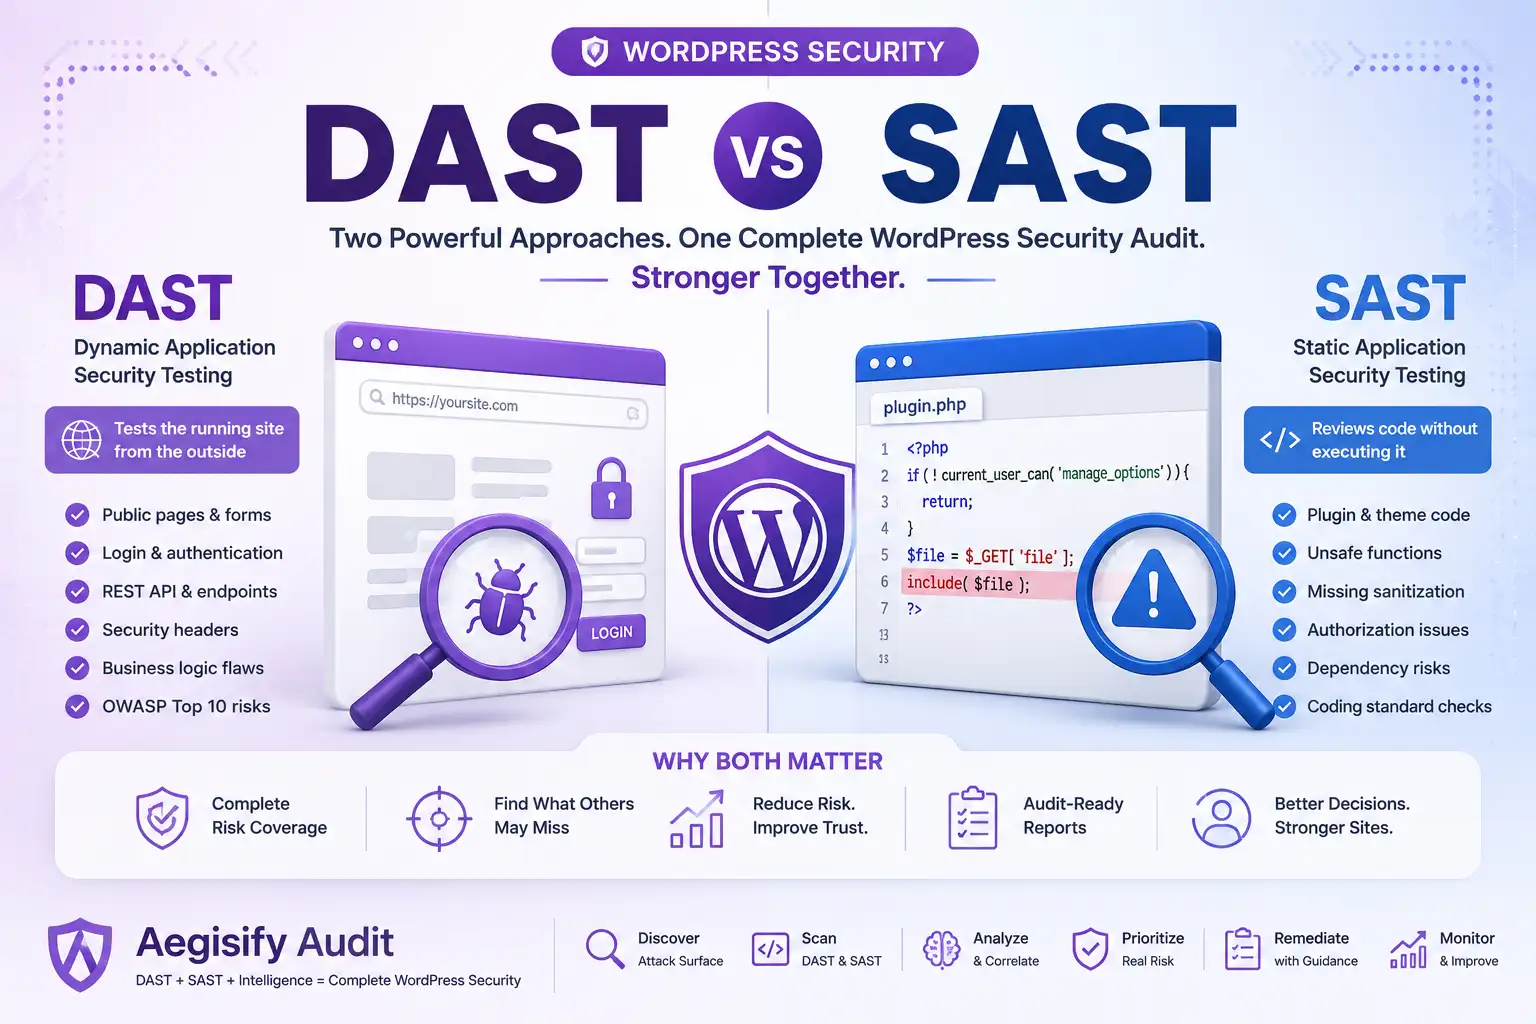
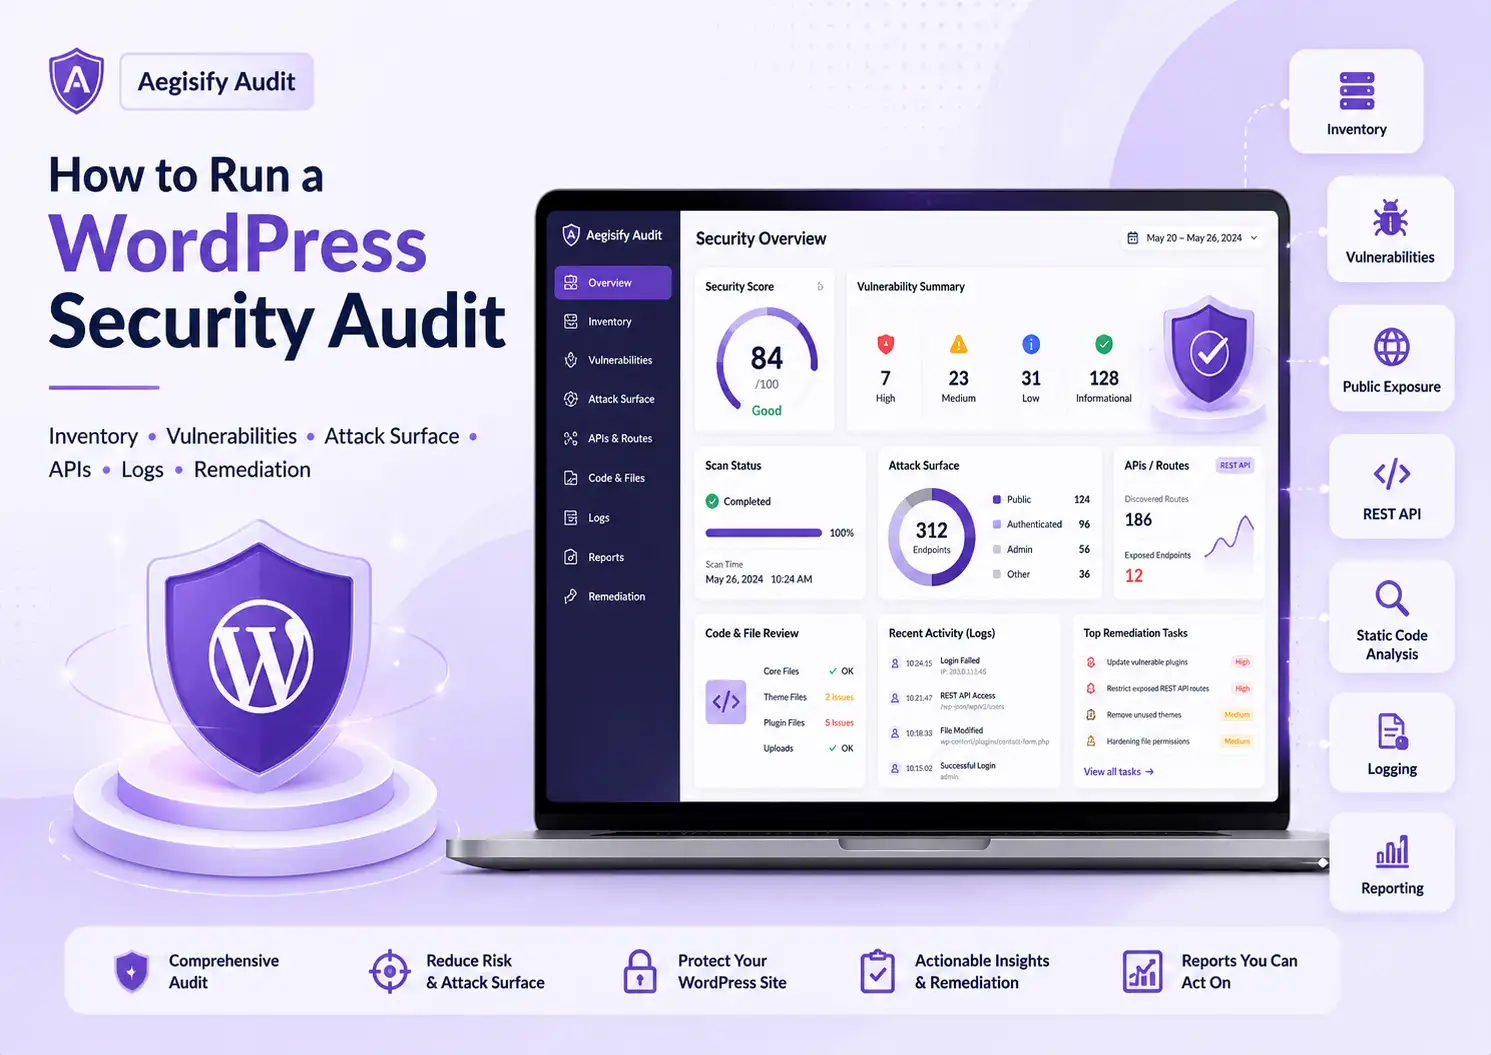
WordPress Security Hardening Audit WordPress Security Hardening Audit: Find Configuration Risk Before It Becomes an Incident A WordPress website can be fully patched and still carry avoidable security risk. The problem is often configuration: public debug output, weak account controls, exposed files, unsafe API behavior, incomplete malware monitoring, permissive settings, or hardening options that were never reviewed after the site changed. ...
Ask Aegisify AI
Aegisify + WordPress security, troubleshooting & free-scan assistant
How can Aegisify AI help?
Ask about Aegisify or WordPress: errors, plugins, security, SEO, compatibility, troubleshooting, comparisons, or launch a free website scan.